 VANKPA

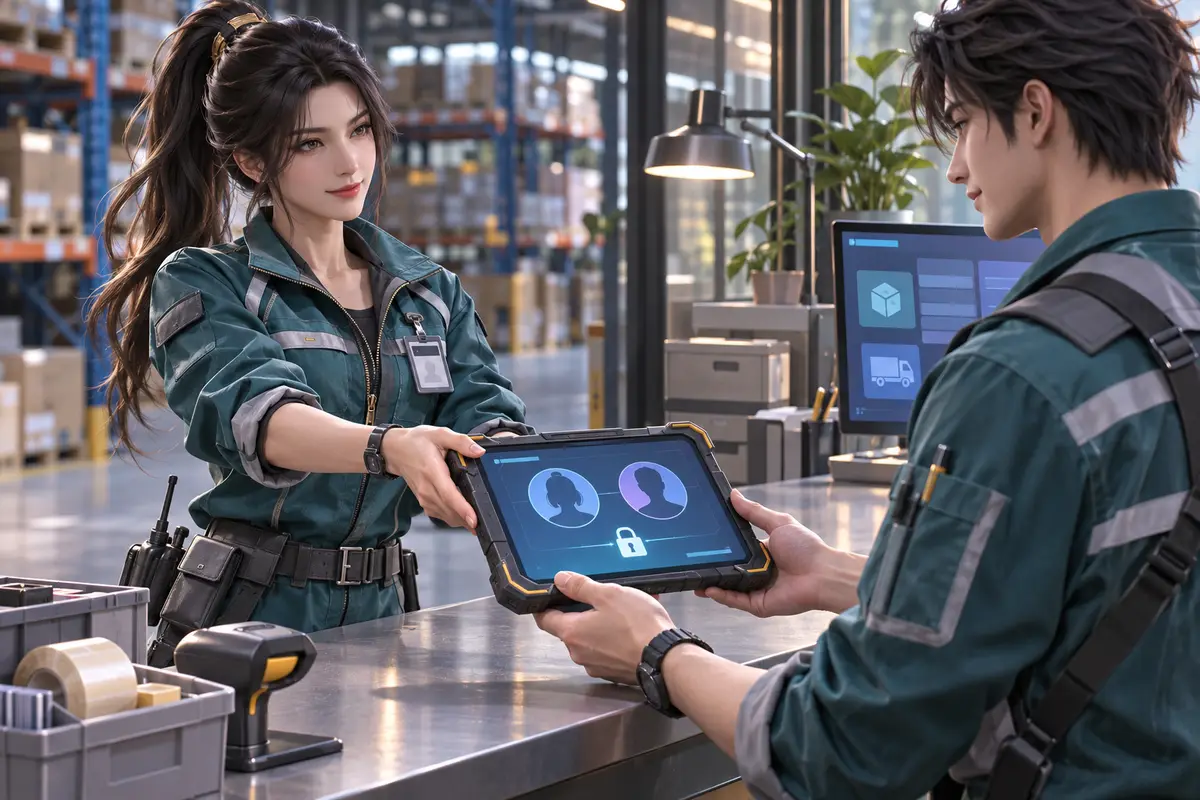
A mobile app may be designed around one person owning one device, while the actual team shares a tablet across shifts. That difference affects sign-in, notifications, saved files, and accountability. Shared-device use needs to be a known requirement rather than an informal workaround.
Make the active identity visible
Show which account or operating role is currently in use and provide a clear sign-out or user-switching route. Use supported individual access where the workflow requires accountability. Do not solve a shared-device requirement by encouraging everyone to use the same password.
Decide what information may remain on the device between users. Cached documents, recent searches, notifications, and downloaded files can expose another person's work even after the main screen changes.
Protect unfinished tasks
Imagine a hypothetical field team handing a tablet to the next shift while a report remains unsent. The app should show whether the report is saved, queued, or tied to the previous user's account. It should not silently submit the work under the next person's identity.
Define how authorized staff can transfer responsibility for an incomplete task. Keep the record of who performed which action, and avoid making local drafts available to every later user by default.
Test the handover conditions
Check user switching with a weak connection, pending uploads, expired sessions, and notifications arriving after sign-out. Verify both the visible screen and locally retained content using the platform's supported testing methods.
Provide a short operating guide for the team: how to finish a shift, confirm pending work, and prepare the device for the next authorized user. Include the approved route for a lost or damaged device.
Start by observing one actual device handoff. The goal is a clear change of responsibility without losing work or allowing the next user to inherit access that was never intended for them.